
GMO Internet Group and Park24 are offering payments to customers after separate cyber incidents in Japan, putting immediate numbers on the cost of breach response even as Tokyo expands its powers to disrupt serious attacks. The cases also show a limit of the new policy: a company’s request for government action is not, by itself, a route to state intervention.
In a Reuters dispatch published October 26, GMO said it would compensate foreign-exchange trading customers for losses arising from unauthorised access and provide a 5,000-yen goodwill payment to all customers. Park24, the operator of the Times car-sharing service, said it planned 3,000-yen payments following a personal-data breach and expected a 5.5 billion-yen extraordinary loss for response costs and compensation.
The reported payments are distinct remedies for distinct incidents, not evidence of a single campaign or a measured nationwide economic loss. They do, however, make the corporate consequences visible: reimbursement, goodwill payments, changes to data handling and accounting charges can arrive before investigators establish a complete technical account of an intrusion.
Two incidents, two forms of customer redress
GMO’s plan has two parts. Customers whose foreign-exchange accounts suffered losses tied to the unauthorised access are to be compensated, while the 5,000-yen payment applies more broadly as a goodwill gesture, according to the Reuters report. The distinction is consequential: compensation is linked to a claimed financial harm, whereas the flat payment addresses disruption and damaged confidence across the customer base.
Reuters also reported that GMO chief executive Masatoshi Kumagai said a party the company believed was responsible had demanded US$50 million in cryptocurrency and threatened to disclose company and customer information. GMO said it would not comply. The allegation is the company’s account of the demand; the available reporting does not independently establish the identity of the party or responsibility for the incident.
Park24’s response is more readily quantifiable. Its projected 5.5 billion-yen extraordinary loss includes its breach response and customer-compensation plan. The company also said it would stop retaining images of identity documents after they have been used for registration verification. That is a practical change to the amount of sensitive material held after onboarding, though the reporting does not establish how much it will reduce future exposure.
Park24’s 3,000-yen payment and GMO’s 5,000-yen payment should not be treated as a comparable measure of incident severity. They are company-set customer remedies with different affected populations, harms and service models. Nor does the 5.5 billion-yen Park24 provision establish an economy-wide cost from cyberattacks; it is a company-specific estimate.
Active cyber defence is not routine breach response
The incidents have unfolded as Japan begins putting parts of its active-cyber-defence framework into operation. An Internet Watch explainer says provisions covering public-private cooperation and access to, or neutralisation of, attack infrastructure took effect on October 1. Other provisions governing use of communications information are expected in autumn 2027, after further implementation rules are prepared.
Those powers are considerably different from the conventional tasks now facing GMO and Park24: notifying users, investigating systems, reimbursing losses and reconsidering what data a service needs to retain. Active cyber defence is designed for preventing grave damage, under legal conditions and oversight, rather than functioning as a general-purpose incident-response service for private companies.
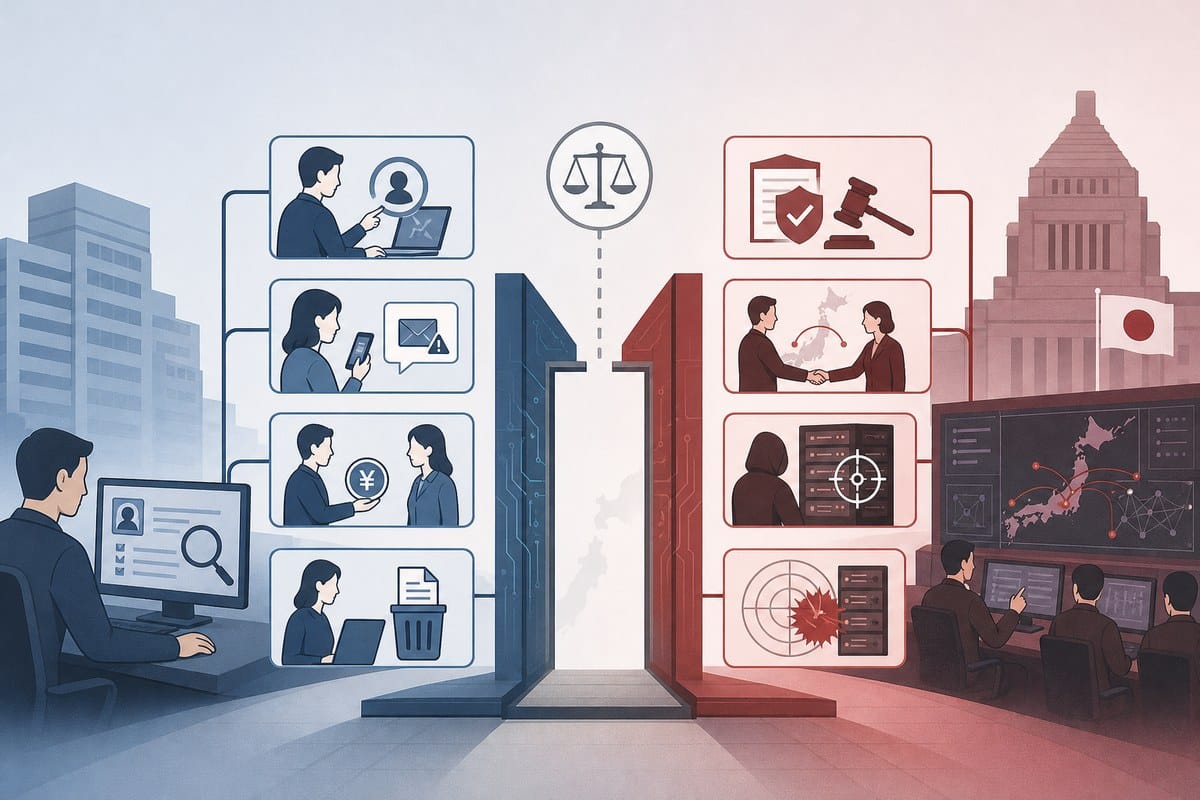
That gap is already visible in GMO’s case. Asahi Shimbun reported that GMO sought application of the framework, but Ritsumeikan University professor Tetsutaro Uehara said the publicly known facts did not appear to meet its high threshold. In his assessment, an FX-related service did not appear to be core infrastructure and the case had not been shown to involve a national-security crisis. That is expert analysis, not a government ruling, but it underlines how narrow the regime may be in early use.
Reuters reported separately that the government planned an emergency cyberattack package and an AI-assisted cyberattack-simulation team intended to identify system weaknesses. The dispatch did not provide technical specifications, operational authority or a deployment timetable for that team. It would be premature to equate a proposed simulation capability with authority to monitor networks, access foreign infrastructure or neutralise an attack.
What the available evidence does and does not show
The Reuters dispatch placed the incidents in a wider period of heightened concern. It cited TrendAI, a Trend Micro unit, as counting 723 cybersecurity incidents in Japan through October 20, already above the annual totals cited for 2025 and 2024. That is a private-sector count reported by Reuters, not an official government tally, and the methodology is not set out in the available account.
It also noted widespread hacking attempts after disclosure of critical PHP vulnerabilities. But GMO did not identify a connection between those flaws and its incident. The chronology may be relevant to the broader threat environment; it is not evidence of a cause. Assigning an intrusion to a particular vulnerability requires forensic findings that have not been made public here.
Asahi’s reporting raises a further technical question about how a compromise could move through shared or virtualised systems. Uehara suggested that GMO’s virtual private-server design may have allowed a breach to spread between users, but said the design needed verification. Without a published forensic report, that remains a hypothesis rather than an established mechanism.
For affected customers, the immediate facts are more concrete than the wider policy rhetoric: GMO has said it will cover qualifying FX losses and make a 5,000-yen payment to all customers; Park24 has planned 3,000-yen payments, a change to identity-document retention and a 5.5 billion-yen extraordinary loss. Japan’s new state powers may become important in a future crisis, but the available accounts do not show they have been used in either case.