
Microsoft has linked the recent ConnectWise Cloud Backup supply-chain compromise to Storm-0940, a group it assesses is aligned with the Chinese state, and says the attackers used an agentic artificial-intelligence framework to accelerate attacks on customer Microsoft 365 environments. The company’s October 21 threat-intelligence report puts unusually concrete numbers around a familiar cloud-security problem: compromise a trusted application with broad access, then use its existing connections to reach many organizations.
Microsoft said the attackers gained control of identities associated with multiple ConnectWise cloud applications and then attempted sign-ins to more than 2,250 Microsoft 365 tenants. That figure is a measure of attempted access, not 2,250 confirmed intrusions. Still, the case shows why software supply-chain incidents involving multi-tenant cloud applications can be more consequential than an ordinary stolen-password event: the application may already have been trusted by customer tenants before the attacker arrives.
From trusted application to downstream tenant risk
The ConnectWise incident was not a compromise of Microsoft’s own systems. Microsoft’s technical account explicitly says its corporate systems, products and services were not compromised. Instead, the reported route was through compromised ConnectWise application identities that could authenticate to customer Microsoft 365 environments.
That distinction is more than public-relations fine print. A multi-tenant application can be granted permissions that let it perform work for a customer without a person interactively signing in each time. Once an attacker controls the application identity or its credentials, it may be able to use that pre-existing trust for app-only access. Microsoft said it observed activity in multiple customer environments that included Microsoft Graph reconnaissance, changes to application credentials and efforts to modify privileges.
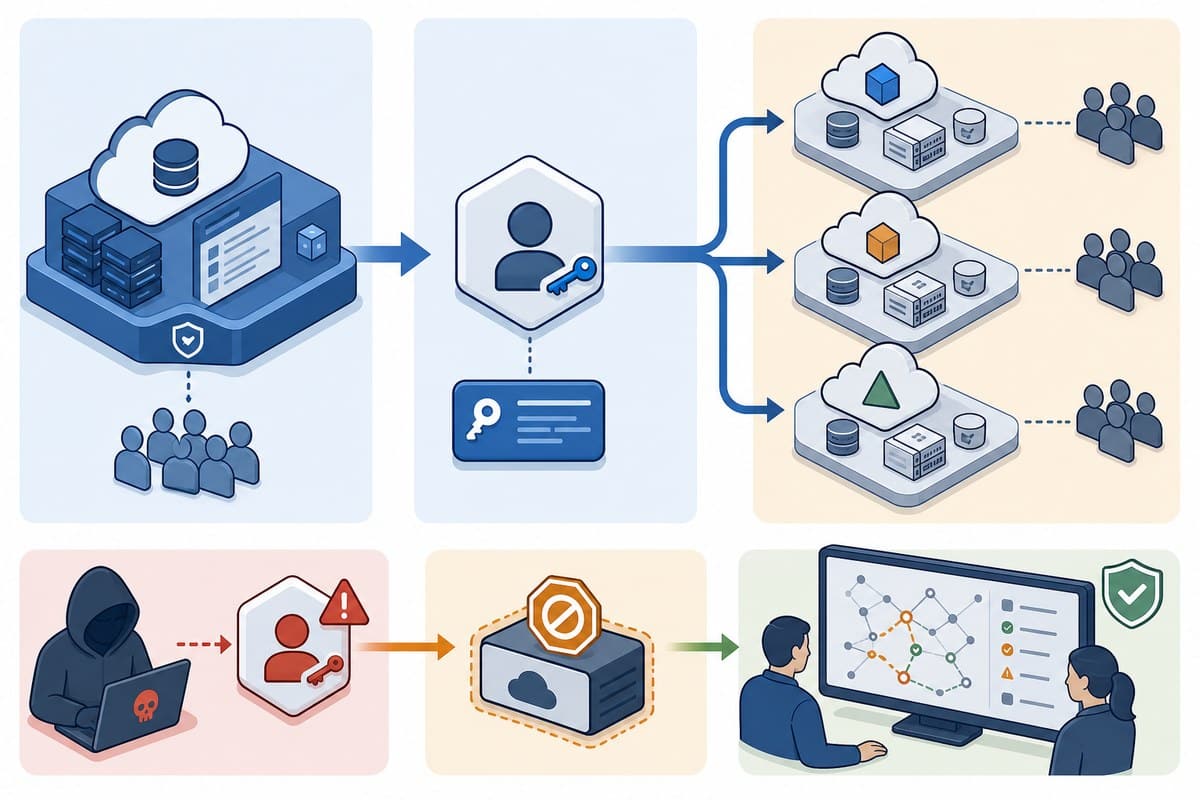
Graph is Microsoft’s interface for working with cloud-directory and Microsoft 365 resources. Reconnaissance through it can help an intruder map users, groups, applications and permissions. Altering an application credential or adding a privilege can be more durable than the original access path. That is why simply disconnecting the affected application is necessary but may not be sufficient if an attacker has already established another authorized-looking route.
What Microsoft says ARTEX changed
Microsoft describes ARTEX as an AI-model-agnostic, multi-agent penetration-testing framework. In this case, the company says Storm-0940 used it from at least September to automate parts of offensive operations against hundreds of organizations worldwide. The tool did not independently carry out an attack; it operated on behalf of the threat actor, according to Microsoft’s assessment.
The reported value of the framework was speed and coordination. Microsoft said it accelerated password spraying, reconnaissance and OAuth application abuse, and that Storm-0940 reached privileged cloud persistence at many organizations. In several cases, Microsoft said, the time from targeting an organization to privileged access was under three hours. That is a compressed window for a security team to spot anomalous authentication, determine whether it is benign and revoke access before the intrusion changes shape.
The AI label should not obscure the underlying mechanics. Password spraying remains a brute-force technique that tries a small number of likely passwords across many accounts, while OAuth abuse exploits the authorization relationships among apps, users and cloud services. Automation has long been part of such operations. Microsoft’s account suggests ARTEX made the sequence faster and more scalable by organizing distinct tasks, rather than introducing a wholly new type of cloud compromise.
An earlier campaign documented by Microsoft illustrates the difference between noisy activity and a successful breach. Between October 10 and October 14, infrastructure associated with the actor targeted 327 accounts at eight organizations and generated more than 151,000 failed logons. Activity peaked at 2,900 failures a minute on October 11, with more than 111,000 failures that day. Microsoft said it observed no successful authentication, token issuance, Graph call or directory change in that particular password-spray campaign.
That evidence should not be folded into the ConnectWise case as proof that every attempted sign-in succeeded. Microsoft said reports of the ConnectWise compromise began surfacing on October 15 and linked publicly reported indicators to infrastructure it had seen earlier. The sequence supports its attribution analysis, but the two sets of numbers answer different questions: one documents a failed password-spray effort; the other records the much broader set of tenant sign-in attempts made after the ConnectWise application identities were compromised.
Containment does not settle the exposure question
ConnectWise suspended affected Cloud Backup connections while it investigated. Reporting by Cybersecurity Dive said the company had found no indication that partner backup data had been compromised. ConnectWise also told customers to keep affected application connections disabled until it gives formal reconnection instructions, according to Anadolu Ajansı.
Those statements establish neither universal safety nor a confirmed theft of customer information. Microsoft cautioned that the presence of the affected application in a tenant, or even successful attacker authentication, does not by itself demonstrate data access or exfiltration. Equally, a tenant that disconnects the application must still investigate whether unauthorized credentials, service principals, permission grants, accounts or directory-role changes remain from earlier activity.
The initial cause of the ConnectWise credential exposure remains unsettled. ConnectWise said it was investigating how credentials were exposed and had not determined whether a product vulnerability played a part, Anadolu Ajansı reported. China’s Embassy in Washington rejected accusations implicating Beijing. Microsoft’s description of Storm-0940 as China-state-aligned remains the company’s assessment, rather than public proof of Chinese government direction.
For customers, the practical issue is therefore broader than restoring a backup integration. Microsoft’s guidance centers on reviewing application authentication and authorization activity, revoking suspicious credentials and grants, and checking for privilege changes or unfamiliar identities. Independent reporting by The Record similarly underscores the unusual downstream reach of a compromise involving a trusted service-provider connection. The incident is a reminder that in cloud environments, the most valuable credential may not belong to an employee at all; it may belong to the application the employee’s organization has already authorized.