
California has begun notifying students and families after an unauthorized party accessed and copied files from a system operated by Educational Testing Service, the contractor that supports the state’s major assessment programs. The California Department of Education says the incident may involve records for students enrolled during the prior three school years, as well as certain former students.
The disclosure is significant not because California has confirmed a precise number of victims—it has not—but because the files may contain a detailed picture of a child’s school life: identity and contact information, enrollment and program records, disability and Section 504 status, English-learner status, and statewide assessment data. ETS began notifying affected students and families on October 16, according to the state’s public announcement, with mailings expected to continue into early November.
Compromised credential opened access to transfer site
California’s account identifies a familiar but consequential failure point: a compromised login credential. According to the Department of Education’s incident information page, an unauthorized party used that credential to enter an ETS-operated secure file transfer protocol, or SFTP, site and copy files at various times between May 22 and September 18.
ETS identified unauthorized activity on September 25. The state says the company then disabled the account involved, took the affected transfer site offline and began an investigation with outside cybersecurity specialists. It has since built a replacement site with enhanced security controls. The California Cybersecurity Integration Center is assisting with digital forensics and incident response, while the state Department of Technology and Governor’s Office of Emergency Services are also supporting the response.
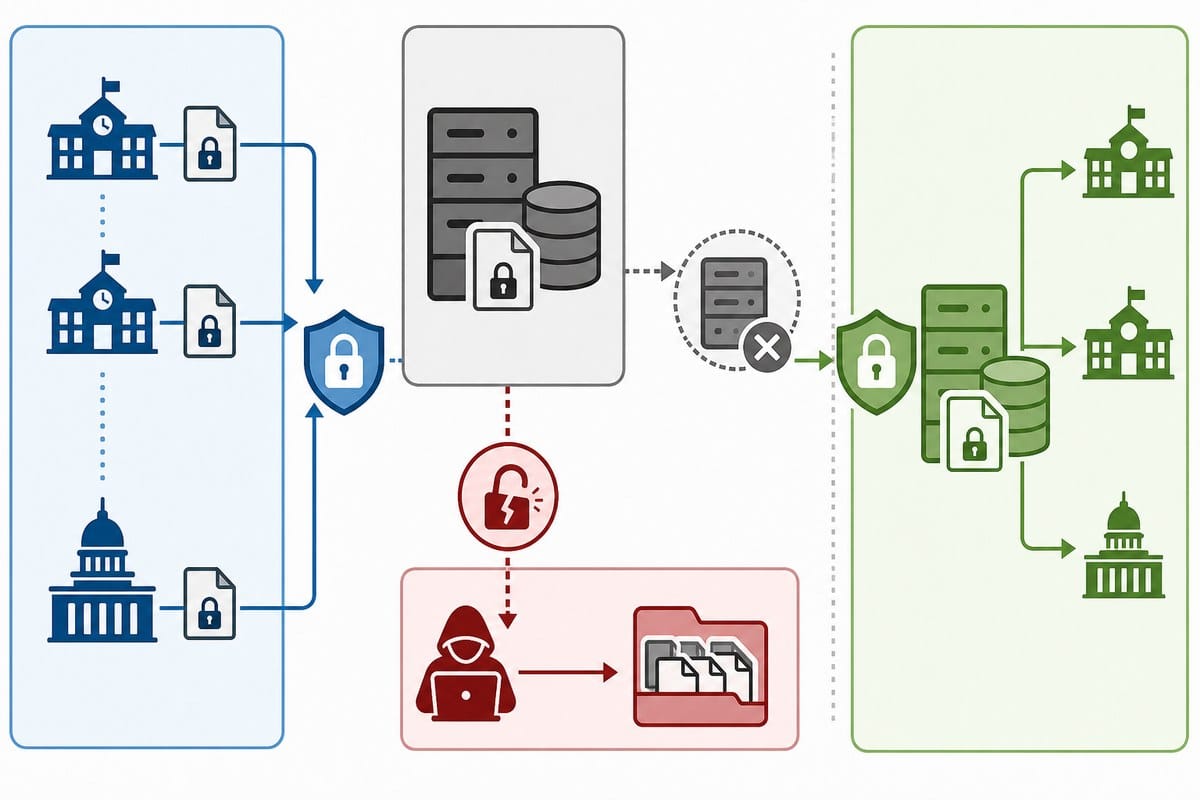
SFTP is commonly used to move large, sensitive files between organizations over an encrypted connection. Encryption in transit, however, does not prevent access by someone holding valid credentials. The state has not identified the unauthorized party or said how the credential was compromised, and it has not described the volume of files copied.
What information may be in the copied files
The data fields vary by individual; California is not saying every affected person had every category of information in the files. Its notice to affected individuals lists names, dates of birth, addresses, school and grade information, state and local student identifiers, demographic information, program-participation records and statewide assessment information among the possible contents.
The list also includes information that can be particularly sensitive in an education setting: English-learner status, disability status and Section 504 status. Section 504 refers to protections and accommodation plans for students with disabilities under a federal civil-rights law. Assessment results and program records may not carry the same immediate fraud risk as a bank-account number, but they can reveal personal educational history that families reasonably expect schools and their vendors to safeguard.
California says several high-risk categories were not involved: Social Security numbers, driver’s license and passport numbers, financial account and payment-card information, passwords, and parent or guardian personal information. Those exclusions narrow the known exposure, but do not make the remaining information trivial. A name, date of birth, address and persistent student identifiers can be sensitive when assembled in one place, particularly alongside disability and academic records.
ETS’s monitoring had not found evidence that the copied information had been made public as of the state’s notice. That is a finding about what had been detected at that point, not a guarantee that the files cannot later be misused or disclosed.
“Millions” is context, not a confirmed breach count
Reports have described the event as affecting millions of California students. A Reuters report carried by The Daily Star cited California enrollment exceeding 5.7 million in the 2025-26 school year. That figure helps explain the potential scale of a statewide assessment contractor incident, but it is not an official count of people whose information was copied.
The Department of Education’s description is broader in some ways and less definite in others. It says the accessed files included information about at least students enrolled during the previous three school years, plus some former students. A student may have appeared in records in more than one year, and the state has not said how many records were taken, how many people those records represent after duplicates are removed, or how many individuals will ultimately receive notices.
That distinction also affects how the episode should be measured. Statewide enrollment is a population figure. A breach count requires a deduplicated accounting of the specific records accessed and the people linked to them. California has published neither accounting, so the numerical scope remains unresolved despite the potentially statewide reach.
Identity-protection offer runs through March
ETS is offering affected current and former students two years of Experian IdentityWorks identity-protection services at no cost, California says. The state lists March 19, 2027, as the enrollment deadline. Families receiving notices should use the enrollment material supplied with their notification rather than assuming that all students in a school or district were included.
The incident also puts renewed attention on the security obligations of vendors that sit between schools and statewide systems. ETS supports California’s CAASPP academic assessments and the English Language Proficiency Assessments for California, known as ELPAC. Such programs require data to move among districts, state agencies and contractors, creating administrative efficiency but also concentrating records in systems whose access controls matter as much as their encryption.
For now, California’s public account establishes the access window, the method described by investigators and the categories of information at issue. It does not establish a deduplicated affected-person count, identify the party behind the intrusion, or provide an individual-by-individual accounting of which data fields were copied.