
Binance temporarily suspended withdrawals on multiple networks after reporting a security incident that it estimated at about $6.3 billion. Two blockchain-analysis firms, working from public transaction records, put the value of cryptoassets moved from Binance-linked wallets between $6.36 billion and $6.43 billion on Oct. 29, potentially making it the largest cryptocurrency theft recorded to date.
The episode is a serious operational test for the world’s biggest crypto exchange by trading volume, but the numbers remain provisional. Binance has said it is working to locate and freeze assets and has pledged to cover losses through its Secure Asset Fund for Users and company funds, according to reporting on the company’s response. That is a commitment, not evidence that customers have already been reimbursed. The exact scope of the withdrawal restrictions and the ultimate recoverable amount were still unsettled.
On-chain trail points to a broad wallet compromise
TRM Labs estimated that attackers took roughly $6.36 billion, while Elliptic calculated $6.43 billion. The $70 million gap is small relative to the scale of the incident and does not necessarily describe a factual disagreement: token prices fluctuate, wallets are identified over time, and each firm used its own tracing cutoff and methodology.
Both firms traced transfers involving Binance-associated wallets on Ethereum, Bitcoin, Tron, the XRP Ledger, Solana, Arbitrum, Avalanche, Optimism, Base and Polygon. Elliptic also identified activity involving NEAR, describing hot wallets across 11 blockchains as having been drained. TRM’s account covers 10 chains. The transfers across multiple wallets and networks indicate the incident was not confined to a single chain or address; Binance has not released a final technical account.
The available analyses describe a particularly consequential sequence on Ethereum. At about 20:20 UTC on Oct. 29, the attacker appears to have used EIP-7702, an Ethereum feature that permits an externally owned account to delegate code execution to a smart-contract address. According to both firms, an attacker-controlled contract was then able to sweep assets from a Binance hot wallet.
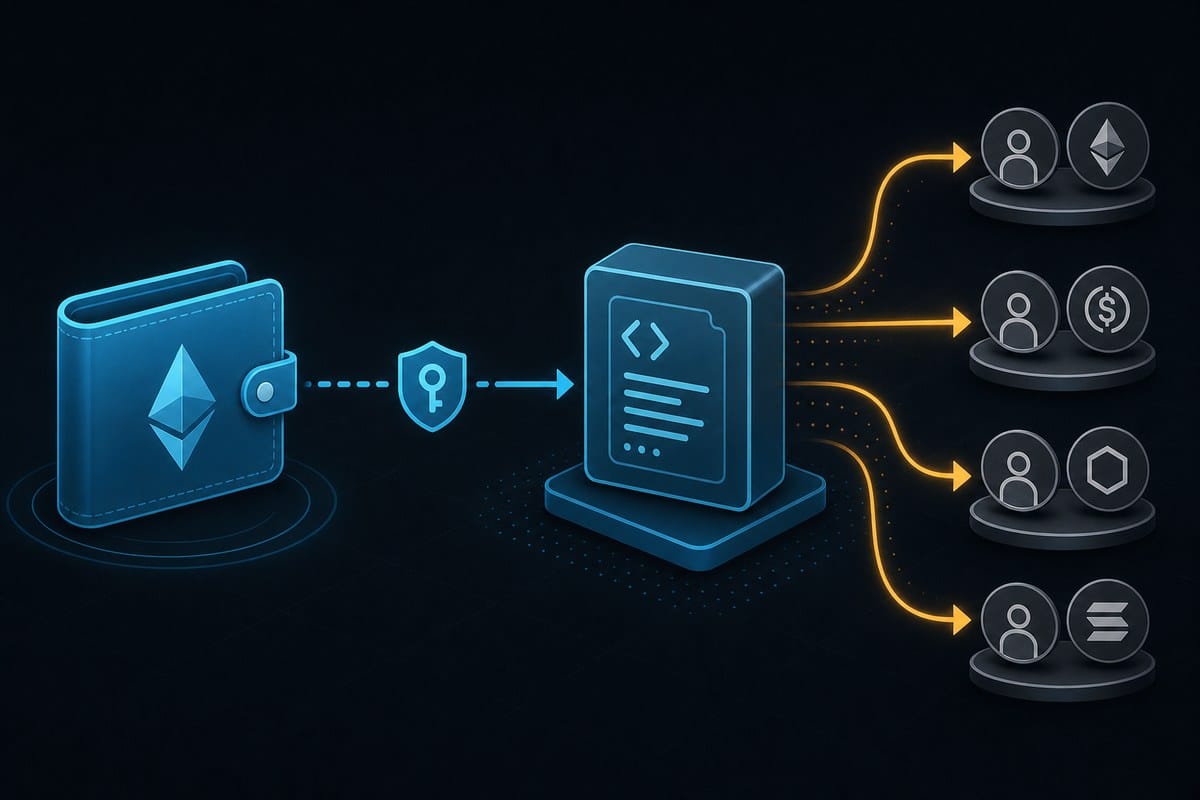
That does not mean EIP-7702 itself created the breach. Delegation is a protocol capability, and the reports indicate that a party had obtained the authority needed to cause the wallet to authorize the relevant transaction. TRM’s assessment is that the compromise most likely reached Binance’s hot-wallet signing infrastructure. Elliptic reported Binance’s preliminary finding that a DevOps engineer’s laptop may have been compromised, providing access to a service container used to submit unauthorized withdrawal transactions. Binance later said it had found additional breach points, according to Elliptic, so the laptop account should not be treated as the final root-cause explanation.
Why billions can be frozen, but not all assets can be stopped
Binance said approximately $3 billion in affected assets had been located or frozen, according to Reuters reporting republished by KRRO. The figure is necessarily time-sensitive. TRM counted about $2.7 billion frozen as of 00:30 UTC on Oct. 30; Elliptic subsequently put the total at $2.84 billion. Those estimates can rise as addresses are identified and issuers or network administrators act.
The freeze totals also reveal an often-overlooked feature of crypto-market infrastructure. Some stolen assets were stablecoins whose issuers retain contractual and technical authority to blacklist addresses. Tether, Circle and Ripple were among entities reported by the analytics firms as taking action or assisting with freezes. The Arbitrum Security Council was also cited in the response.
Bitcoin and ether work differently. Neither has a central issuer able to invalidate a particular holder’s coins. Once those assets move, recovery generally depends on investigators tracing them, exchanges and other intermediaries blocking deposits, or authorities obtaining cooperation and legal remedies. A token’s apparent liquidity, in other words, is not the same as an attacker’s ability to convert it into spendable value.
Freezing controls can limit laundering and improve recovery prospects, but they do not turn preliminary measurements into settled balances. An address may hold a blacklisted stablecoin while other assets remain mobile; funds can also be split, swapped or transferred before a response reaches every relevant service. The useful figure at this stage is not a single recovery percentage but the fact that several billion dollars were subject to intervention unusually quickly.
Attribution and restoration remain unresolved
Both analytics companies connect the attack to North Korean state-linked activity, but their conclusions should be read as intelligence assessments rather than official attribution. Elliptic said North Korea-linked involvement was likely. TRM Labs said it assessed with high confidence that TraderTraitor, a North Korean hacking unit, was responsible. Neither account cited an official law-enforcement finding establishing responsibility.
The reported timeline shows preparatory activity on Oct. 28, including small transactions funded through Tornado Cash and testing or deployment of attack code, followed by transfers beginning around 20:05 UTC on Oct. 29. The Ethereum delegation and sweeping transaction followed minutes later, while further activity affected wallets on other networks later that evening. This sequence helps explain why analysts view the event as a coordinated multichain operation rather than an isolated erroneous transfer.
Binance kept deposits operating while it worked through the withdrawal interruption, according to contemporaneous reports. A restoration timetable has been reported, including comments that withdrawals might return before Sunday, but no directly available Binance status announcement confirms a completion time. The exchange’s immediate task is therefore more than reopening a service: it must establish which signing systems were exposed, preserve a traceable record of stolen assets and show that resumed withdrawals are not dependent on the same compromised path.